Understand your application’s security. Act with the full picture.
Farion connects security findings with your code, dependencies, and deployed versions—giving your team the context to investigate vulnerabilities, coordinate remediation, and verify fixes in production. Manage software inventories, SBOMs, and license obligations in the same application-security platform.
One understanding of your application. Connected across every capability.
Farion’s proprietary data-flow engine uses native compiler tooling to follow inputs across functions, files, and dependencies. Its evidence stays connected to findings, runtime tests, and remediation. The shared software inventory brings SBOMs and license compliance into the same application context.
Application code
Functions, files, and code pathsDependencies
Direct and transitive librariesVulnIntel
Advisories, EPSS, and CISA KEVPolicies & standards
Policies and compliance requirementsFarion
Data Flow Engine
CODE · DATA · CONTEXTExploitability Analysis
Code paths and exploitabilitySupply Chain Security
Dependencies, SBOMs, and VEXVulnerability Management
Findings, fixes, and deploymentsActive Verification
Targeted tests and runtime evidenceSoftware License Compliance
License policies and review evidenceApplication code
Functions, files, and code pathsDependencies
Direct and transitive librariesVulnIntel
Advisories, EPSS, and CISA KEVPolicies & standards
Policies and compliance requirementsFarion
Data Flow Engine
CODE · DATA · CONTEXTShared application context
Code paths, dependencies, findings, and deployed versions
Less triage
Only relevant, reachable vulnerabilitiesClearer priorities
With data-flow and context analysisFaster fixes
With concrete evidence and recommendationsSecure your applications. Keep the context.
Investigate vulnerabilities, protect your software supply chain, coordinate fixes, verify findings, and manage license compliance with the evidence connected.
Find what attackers can exploit.
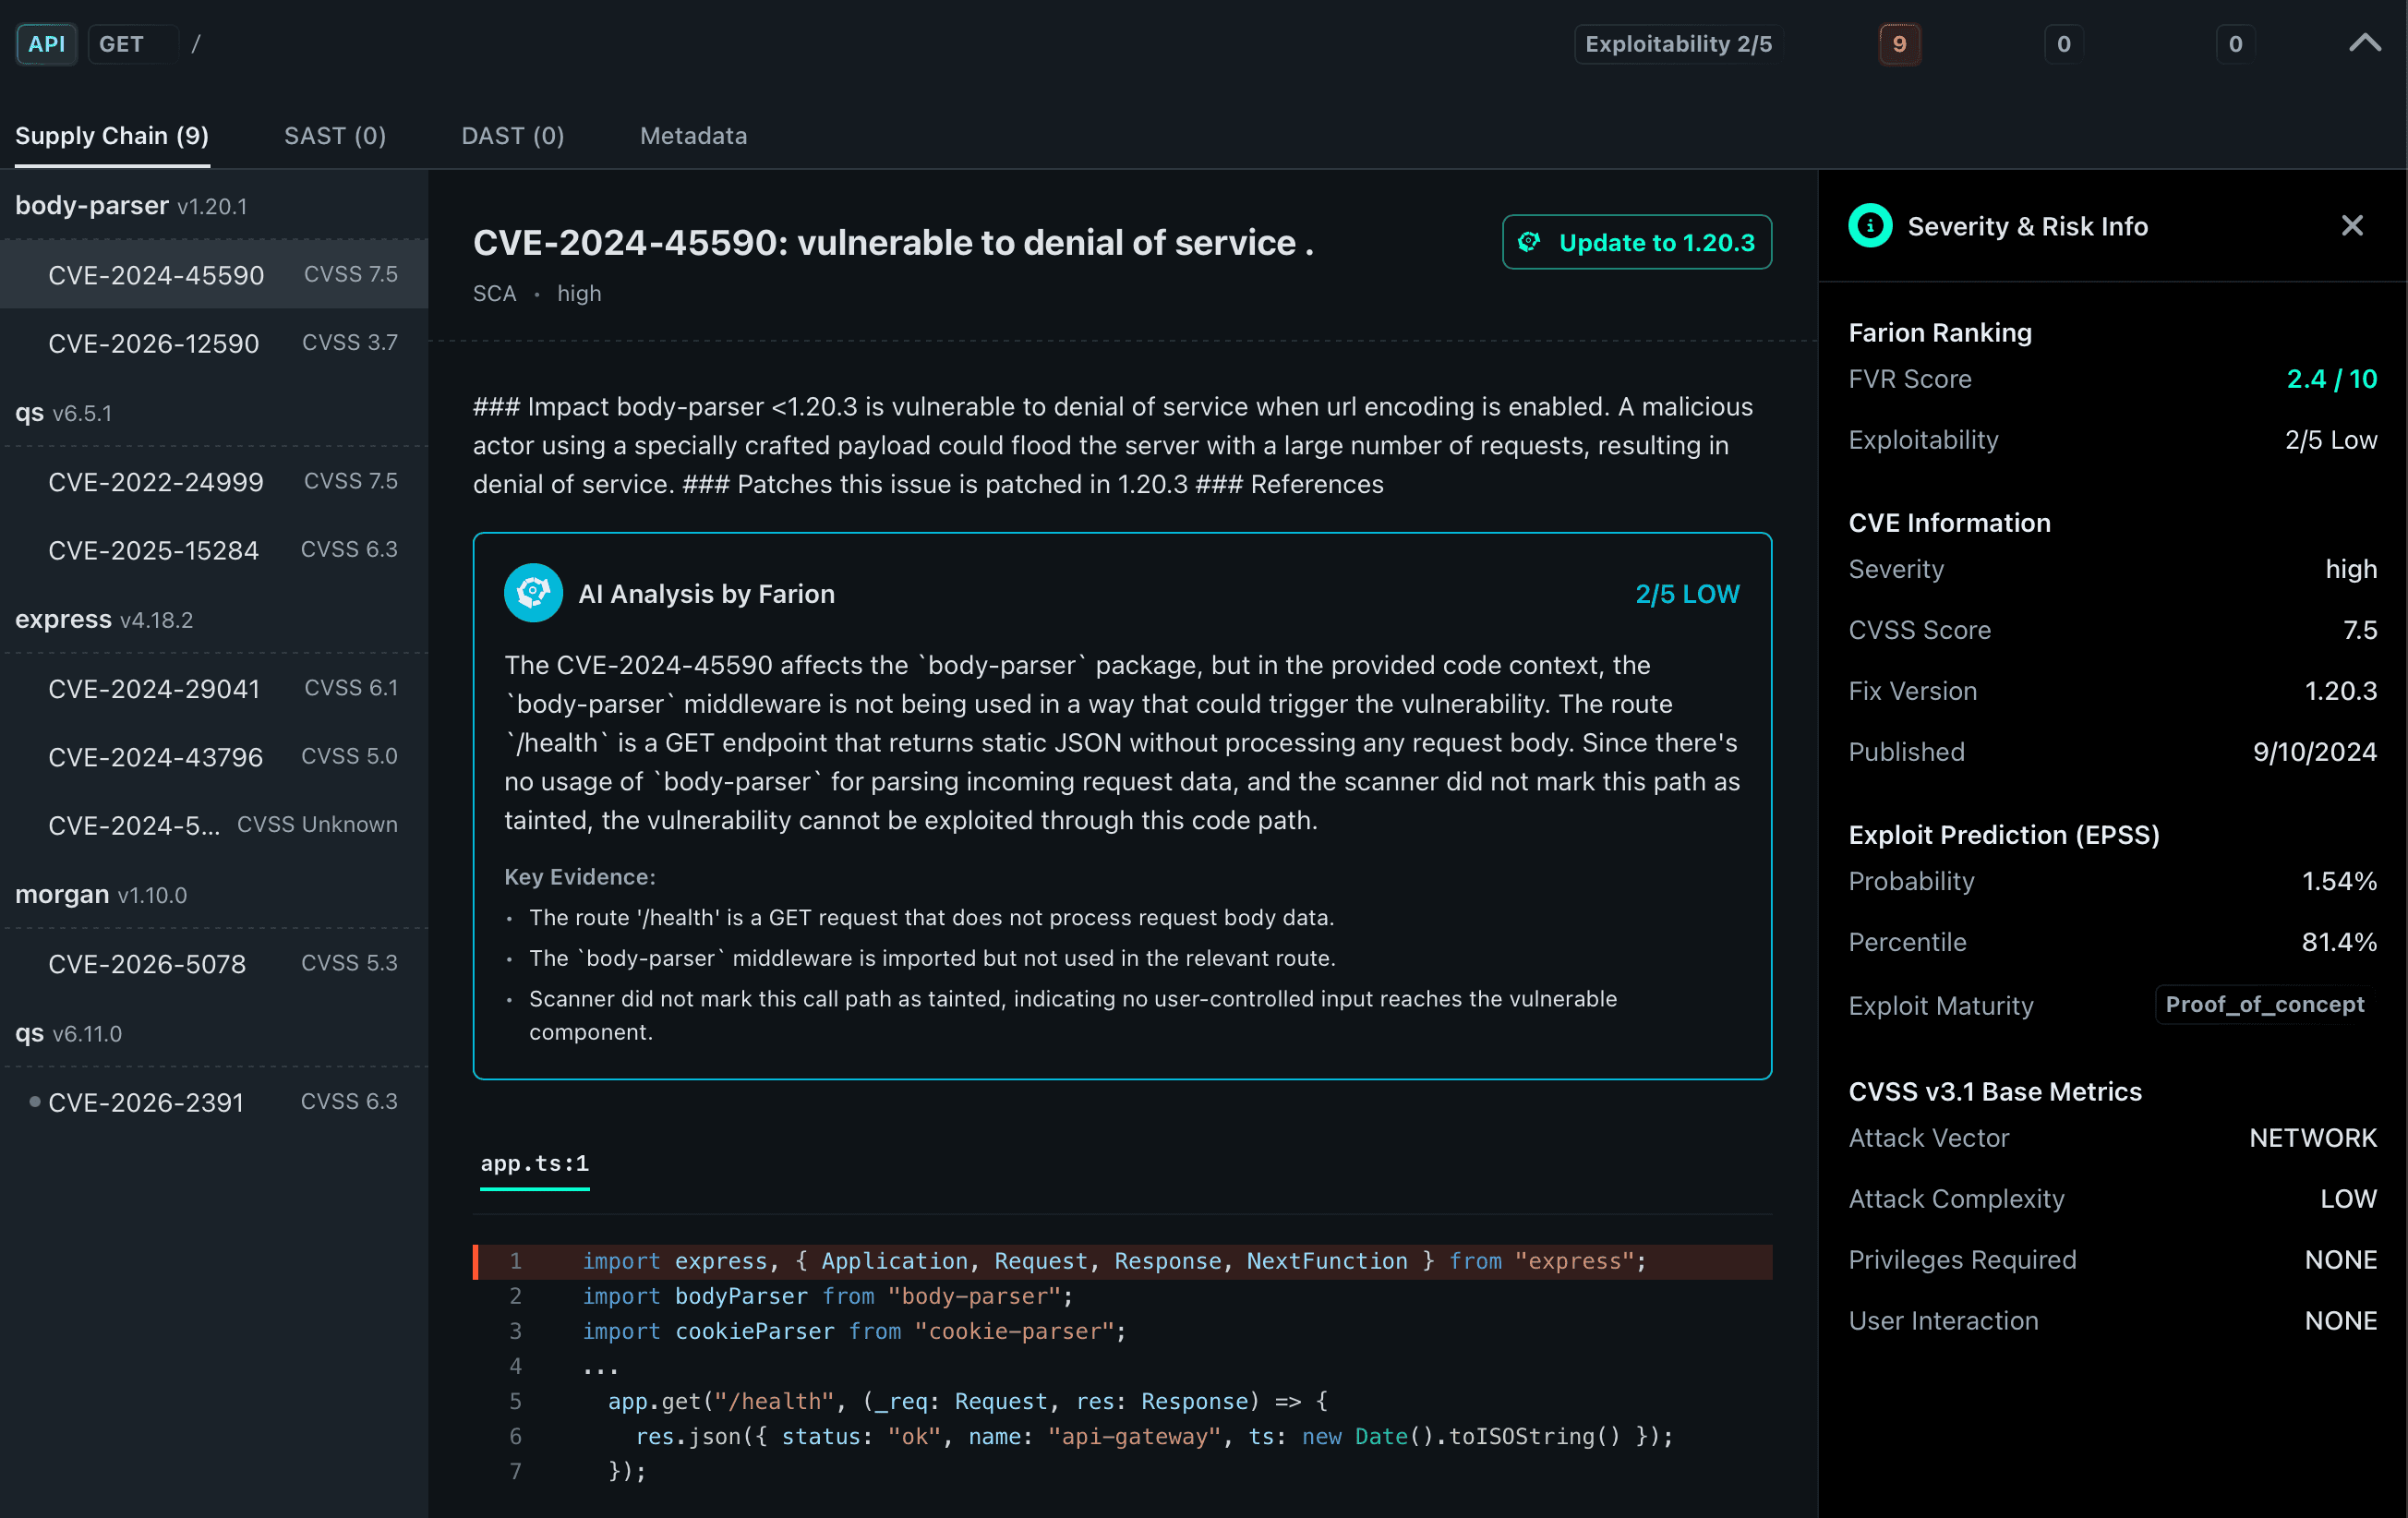
Trace attacker-controlled input
Follow values across functions, files, and dependencies into vulnerable operations.
Assess code and dependency vulnerabilities
Combine data-flow evidence, reachability, and vulnerability intelligence in the application that uses the code.
Inspect the evidence behind the verdict
Review the affected route and source code, with Active Verification adding evidence from the running application.
Secure the software you ship.
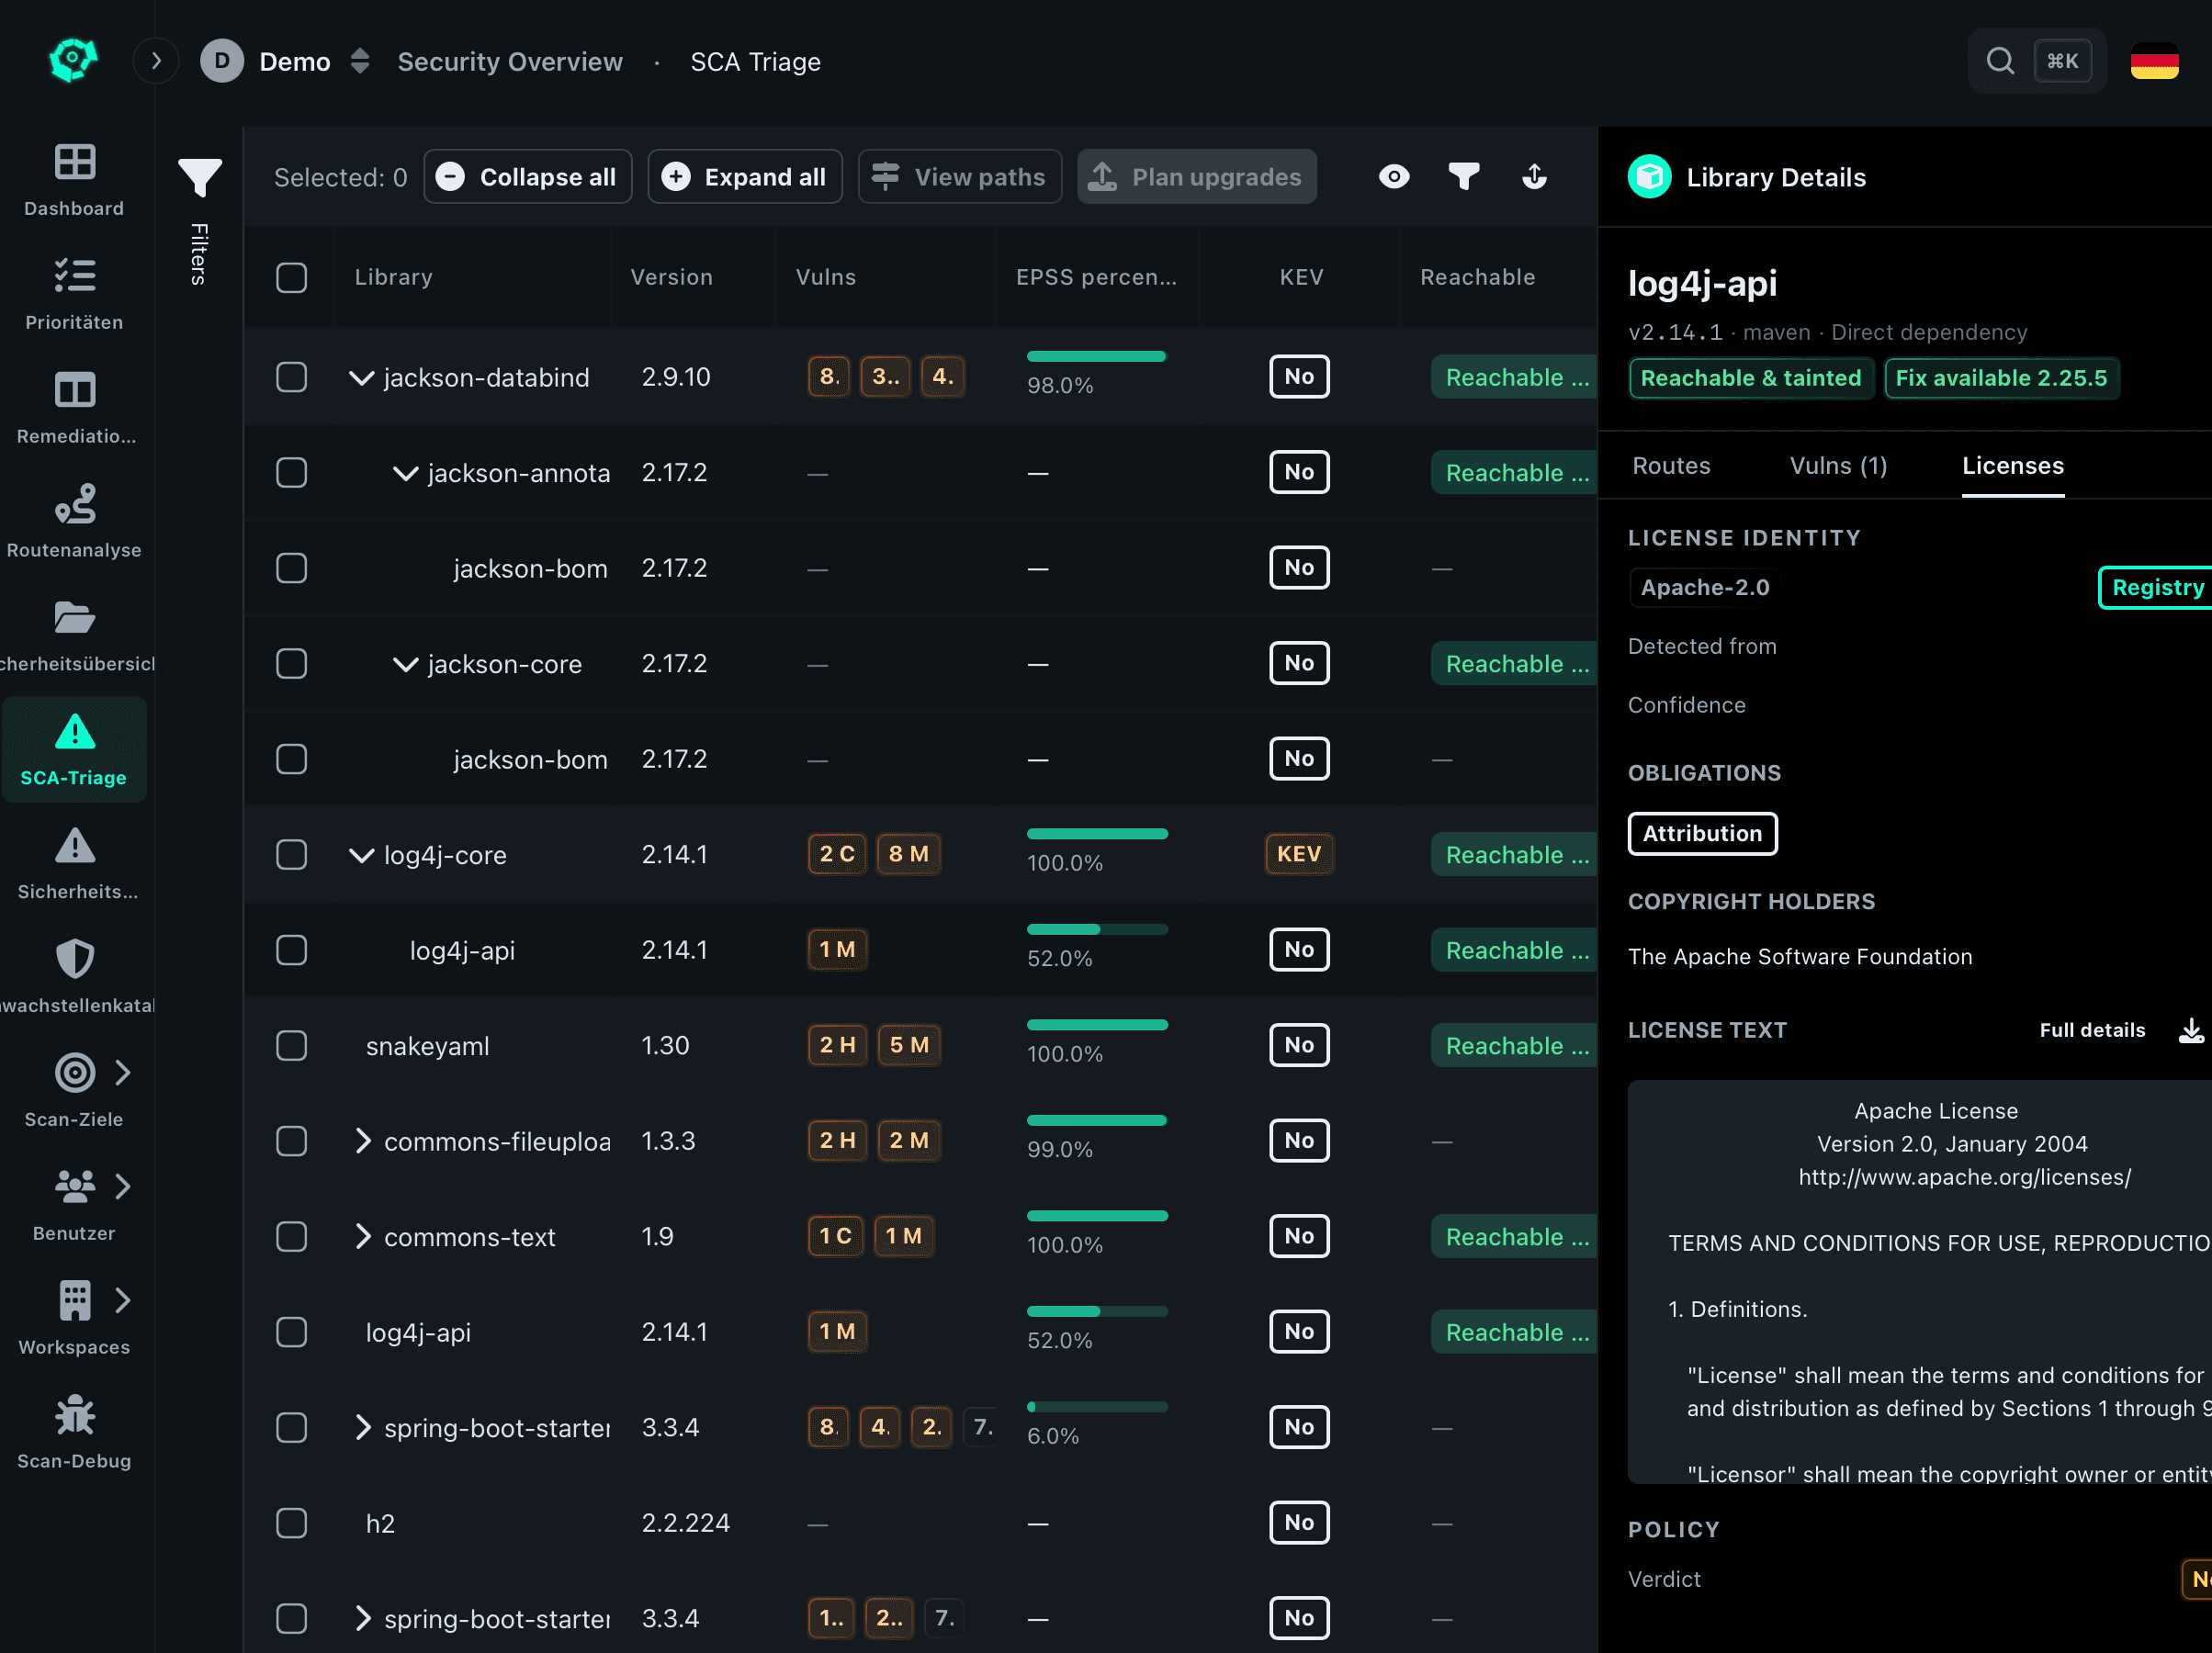
Search your complete software inventory
Investigate direct and transitive dependencies across source code, imported SBOMs, containers, and VMs.
Find affected applications and available fixes
Connect package advisories to application routes, vulnerable functions, exploit signals, and remediation options.
Share SBOMs and vulnerability assessments
Export CycloneDX or SPDX SBOMs and VEX for application dependencies from the inventory you investigated.
Manage every finding. Track every fix.
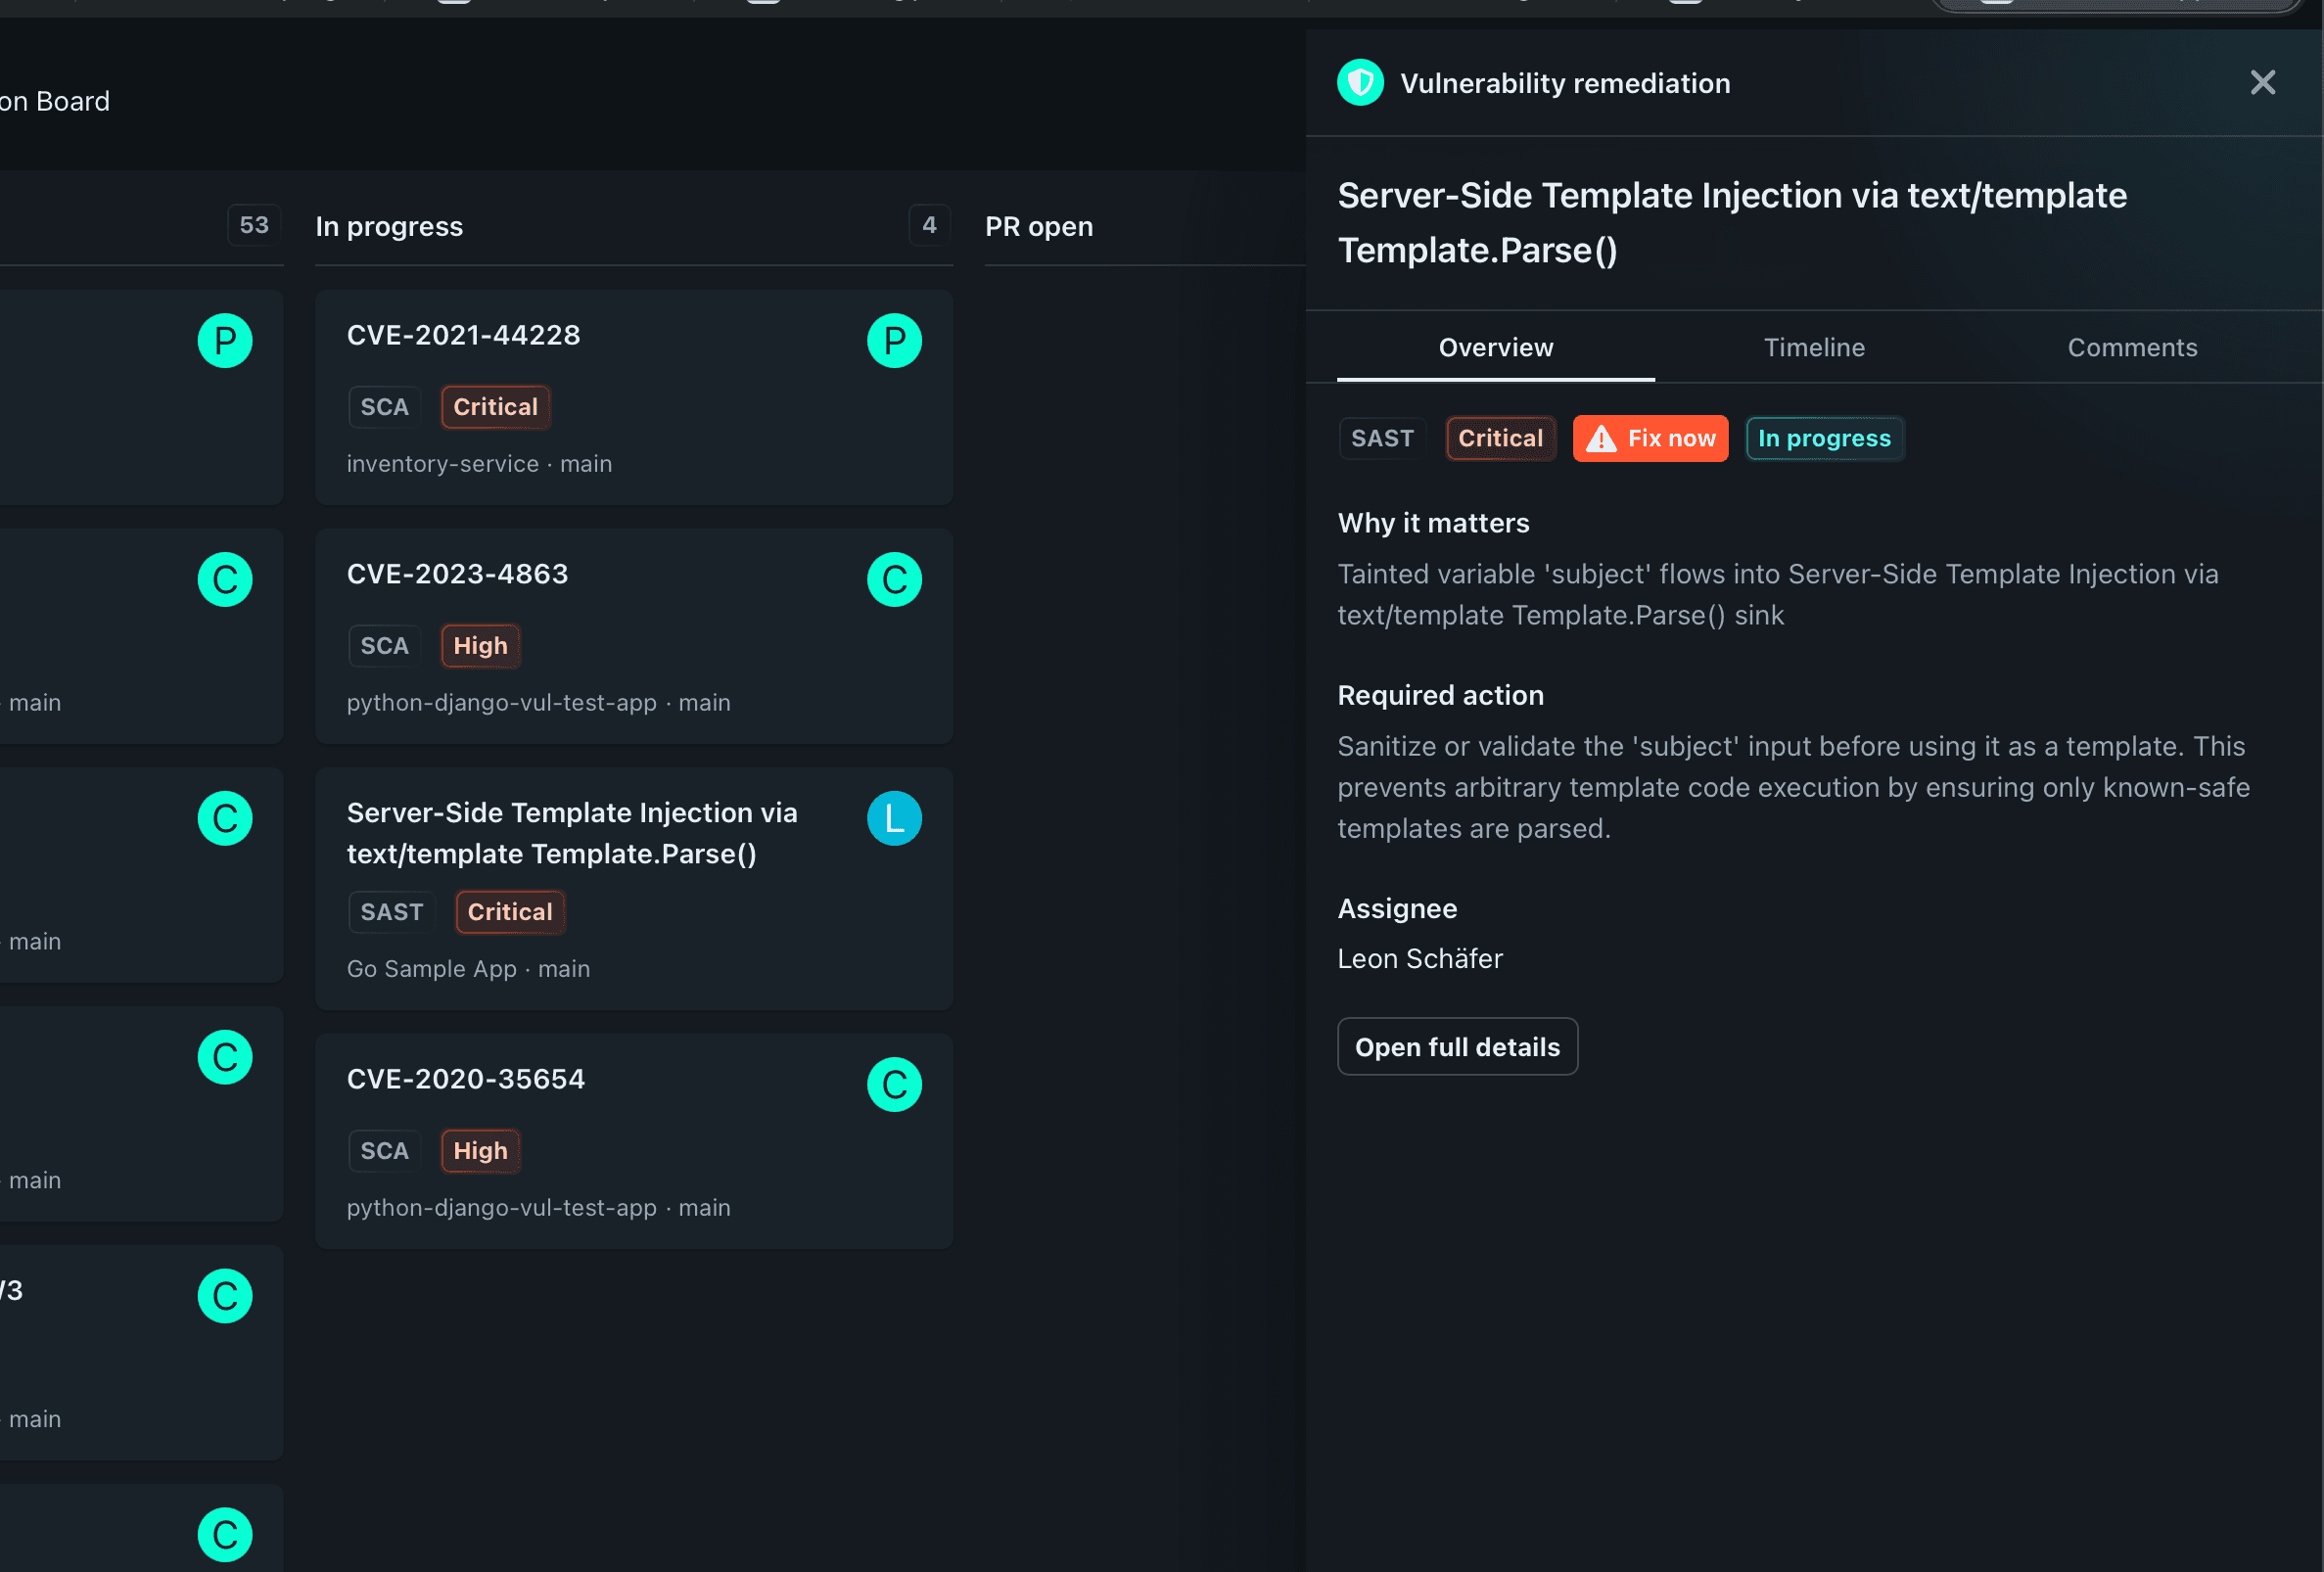
Coordinate remediation with your team
Assign owners, set priorities, and track the work on the remediation board.
Reassess risk when the evidence changes
Keep vulnerability updates, exploitability assessments, data flows, and verification results with the finding.
Follow affected versions into each environment
See where a vulnerability remains and whether the fix has reached development, staging, or production.
Keep the decision and its history together
Review comments, assignments, pull or merge requests, and deployment events in the same finding record.
Test the vulnerability. See the runtime evidence.
Turn a static finding into a targeted test
Use its route, parameter, vulnerable operation, and data flow to generate the test and payload.
Include authenticated application paths
Configure an authorized target and authentication to test protected routes in the selected environment.
Review the result with the original finding
Inspect requests, responses, and observations alongside the code evidence to inform assessment and remediation.
| Route Path | Exploitability | SCA | SAST | DAST | |
|---|---|---|---|---|---|
APIPOST/api/auth/login | 5/5 | 7 | 2 | 2 | |
A07:2021 – No rate limiting on authentication endpointCWE-307: Improper Restriction of Excessive Authentication Attempts DAST medium The /api/auth/login endpoint does not implement rate limiting or account lockout. An attacker can perform unlimited login attempts for credential brute-forcing. Target EndpointPOST https://shop.example.com/api/auth/login Attack DetailsPayloadEvidenceAll 100 requests returned HTTP 401 in ~0.8s avg response time with no rate limiting headers (X-RateLimit-*). No CAPTCHA or account lockout triggered. | |||||
APIGET/api/users | 4/5 | 7 | 2 | 1 | |
APIPUT/api/users/:id | 4/5 | 5 | 1 | 0 | |
APIDELETE/api/users/:id | 4/5 | 4 | 1 | 0 | |
APIGET/api/restaurants/…/menu | 3/5 | 5 | 1 | 0 | |
APIGET/api/restaurants/feed | 3/5 | 5 | 0 | 1 | |
APIPOST/api/payments/checkout | 3/5 | 3 | 1 | 0 | |
APIPOST/api/auth/reset-password | 3/5 | 3 | 1 | 0 | |
APIGET/api/users/…/profile | 2/5 | 2 | 1 | 0 | |
APIGET/api/admin/dashboard | 2/5 | 2 | 0 | 0 | |
APIPOST/api/orders | 1/5 | 1 | 1 | 0 | |
APIPUT/api/orders/…/status | 1/5 | 1 | 0 | 0 | |
APIGET/api/restaurants/:id | 1 | 0 | 0 | ||
APIGET/api/orders/…/track | 1 | 0 | 0 | ||
APIGET/api/search/export | 1 | 0 | 0 | ||
APIGET/api/orders | 1 | 0 | 0 | ||
APIGET/api/health | 0 | 0 | 0 | ||
APIGET/api/config/features | 1 | 0 | 0 | ||
Control license risks. Meet your obligations.
Inspect the licenses that actually ship
Analyze license files and package contents across direct and transitive dependencies, beyond registry metadata.
Apply your organization’s license policy
Identify accepted, restricted, and prohibited licenses. Review multiple licenses and conflicting information with the evidence attached.
Understand attribution and redistribution duties
Review notice, attribution, source-disclosure, and redistribution obligations in the context of the affected applications.
Export evidence for compliance reviews
Share detected licenses, supporting files, obligations, and policy results with the dependency and application context.
See the full picture of your application.
Walk through your code, dependencies, findings, and deployed versions with our technical team. See how the connected evidence supports remediation and license reviews.